ASOS confirms hacker accessed customer names and contacts after impersonating trusted contact
The retailer said basic personal data of millions of customers was accessed, but payment details were not compromised.
By Felo News Desk · Published
ASOS said an unauthorised party accessed basic personal information of millions of customers after impersonating a trusted contact to obtain an employee’s login credentials, according to statements to customers and reports by The Guardian and the Evening Standard.
What happened
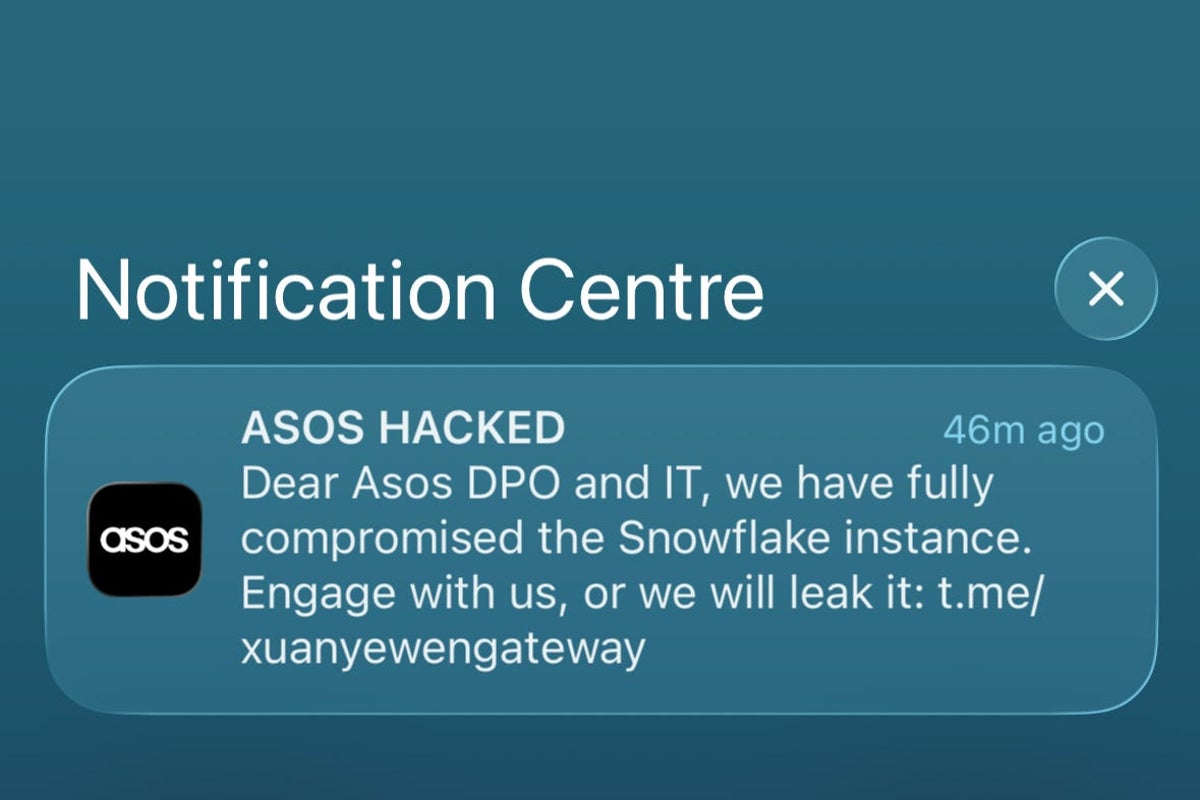
On Tuesday, ASOS customers received a mobile‑app notification titled “Asos hacked” that linked to a Telegram account. The message claimed the retailer’s Snowflake data‑warehouse had been fully compromised. After a 48‑hour investigation, ASOS confirmed that the hacker used the stolen credentials to view names and contact details of customers, as well as “certain non‑personal account‑related information”. The retailer said no payment‑card data or passwords were accessed. The incident triggered a roughly 10% drop in ASOS shares on the London Stock Exchange.
What the reports add
The Guardian reported that the hacker gained access by impersonating a “trusted contact” to obtain login details for an employee account, and that the breach was discovered after the Telegram‑linked alert was sent to app users. The Evening Standard added that the message sent to the Telegram account read: “Dear ASOS DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it.” Both outlets noted that ASOS locked down the affected third‑party platforms immediately and involved internal and external cyber experts, as well as law‑enforcement authorities.
What was said
ASOS told customers in an email on Thursday: “We discovered that an unauthorised party gained access to an ASOS employee account by impersonating a trusted contact to obtain login credentials. Those credentials were then used to access information on certain third‑party platforms used by ASOS.” The statement, quoted by both The Guardian and the Evening Standard, also urged customers to remain cautious of unexpected messages or calls claiming to be from ASOS.
How it came about
Earlier coverage by Felo News on 6 October described the initial push notification and the claim that the Snowflake instance was compromised, noting that personal details of some of ASOS’s 16.5 million customers may have been accessed while payment data was safe. The current reports confirm the same breach, adding details about the impersonation tactic and the 48‑hour investigation that followed.
Key facts
- ASOS customers received a mobile‑app notification titled “Asos hacked” linking to a Telegram account. (theguardian.com)
- The hacker accessed names and contact details of millions of customers but not payment‑card data. (standard.co.uk)
- ASOS shares fell about 10% after the breach was disclosed. (theguardian.com)
Timeline
- 2026-10-06 — ASOS sent push notification claiming Snowflake breach; initial reports of personal data exposure.
- 2026-10-06 — ASOS shares fell 14% after notification, per earlier Felo coverage.
- 2026-10-08 — ASOS confirms hacker accessed customer names and contacts after impersonating trusted contact.
Sources
- [1] theguardian.com
- [2] standard.co.uk