Brief
ASOS confirms data breach after hackers used app to send rogue notification
The UK retailer disclosed that a breach of a Snowflake‑hosted database exposed personal details of millions of customers.
By Felo News Desk · Published
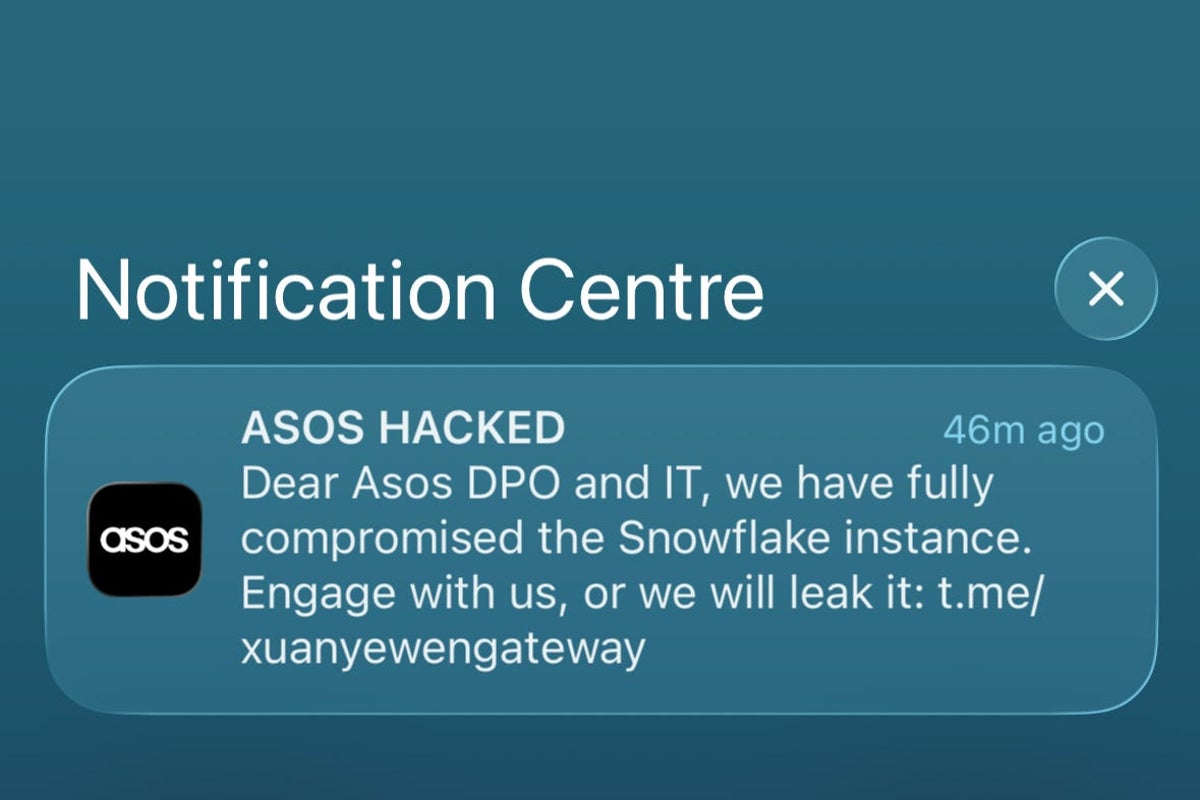
ASOS told the London Stock Exchange that hackers broke into a third‑party platform used for customer communications, stealing names, home addresses, phone numbers and email addresses, as well as profile notes such as search queries. The breach was highlighted when the attackers used the company’s own mobile‑app notification system to send an unauthorised message that warned the data protection officer and IT department that the Snowflake instance was "fully compromised" and threatened to leak the data.
The notification, posted by the group calling itself Xuanye, claimed the hackers had impersonated a trusted contact to obtain login credentials for the Snowflake instance. Snowflake said its own systems were not breached, and it is unclear whether multi‑factor authentication protected the ASOS instance. ASOS, which serves about 17 million customers, said payment‑card details were not affected.
Key facts
- Hackers accessed names, addresses, phone numbers and email addresses of ASOS customers (techcrunch.com)
- The breach was announced via an unauthorised in‑app notification sent by the attackers (techcrunch.com)
- ASOS uses Snowflake to host the compromised data, but Snowflake reports no breach of its own systems (techcrunch.com)
- Payment‑card information was not compromised according to ASOS (techcrunch.com)
- The hacking group identified itself as Xuanye and claimed to have impersonated a trusted contact to obtain credentials (techcrunch.com)
Sources
- [1] techcrunch.com — originally reported as “Asos confirms breach of customer data after hackers send rogue app notification”